We thought Taylor Wessing made a manual mistake with a GDPR request. We were wrong. It’s an automated, firm-wide catastrophe.
The Breach: Elite law firm Taylor Wessing is using an outdated script to “redact” sensitive PDFs, masking data visually but leaving the text fully readable underneath.
The Scale: Evidence suggests this vulnerability has affected their corporate clients (including giants like Pfizer, Just Eat, Chubb, and SAP) since 2019.
The Hypocrisy: While leaking massive amounts of data, their lawyers issue baseless criminal threats to citizens making lawful GDPR requests.
A few days ago, as a spin-off to our massive cybersecurity exposé on How Valve Profits From 70M+ Stolen Steam Accounts, we published an article documenting a catastrophic legal blunder.
We revealed how the elite, high-priced lawyers at Taylor Wessing (specifically Dr. Patrick Zurheide and Dr. Tobias Schelinski) accidentally leaked 830 pages of highly sensitive, de-anonymized Steam user data while trying to defend Valve Corporation against a routine GDPR request.
We joked that my dog, having precisely zero data breaches on her resume, was officially better at data protection than a Salary Partner with a PhD in IT Law.
My dog is now winning 2–0.
Meet our Chief Data Protection Officer. 0 data breaches. 100% better at using PDFs than Taylor Wessing.
After publishing the first piece, we had a long, hard think. We looked at those 830 pages of black rectangles. We realized something fundamental about corporate lawyers: they are generally too self-important to manually draw black boxes on 800+ pages. Doing that by hand would give you a severe case of digital hemorrhoids.
No, they didn’t do it manually. They used a script. And that’s when the joke stopped being funny, and became a systemic, global cybersecurity crisis.
The Cheap Software Behind the Elite Facade
Here is the technical reality of what these lawyers — who think they are richer, smarter, and more important than Valve’s own users — actually did.
To save money on proper, enterprise-grade data sanitization software, their systems rely on a generic, outdated library: Aspose.PDF for .NET 20.8.
The core issue is that their script uses this outdated software to draw black vector rectangles (using re/f operators in the PDF code) over text coordinates. What it should be doing is properly sanitizing and deleting the underlying text layer (using BT/ET operators).
It creates a visual mask on your screen. But the raw data? It remains 100% accessible beneath it.
// The Math on the Scale of this Catastrophe:
Dr. Patrick Zurheide alone likely processes roughly 100 to 300 GDPR requests a year. For the few users who don’t immediately surrender to his initial wave of legal threats and delays, he eventually sends them the “brilliance of his experience” — a legal response document that consists of 94% black rectangles.
But this is not Malevich’s “Black Square”. It is just a cheap vector shape. Remove it.
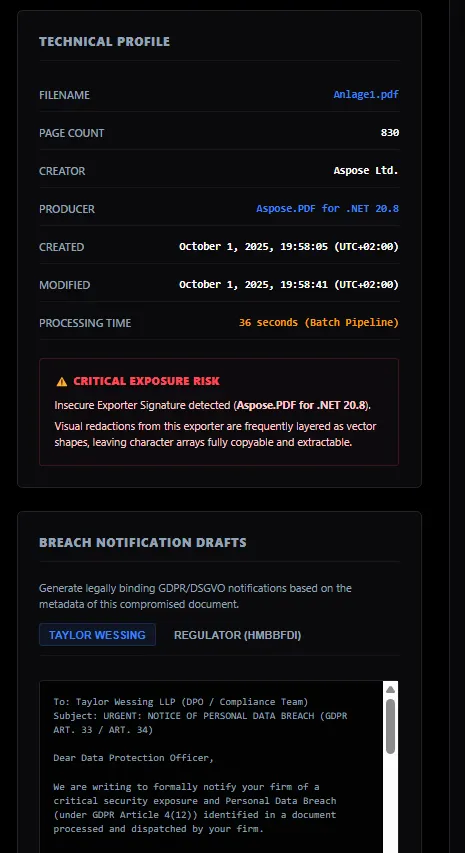
Forensic metadata extraction of Taylor Wessing’s 830-page response. The “36 seconds” processing time is the smoking gun: they didn’t redact manually; they used an automated, vulnerable script.
The Blast Radius: Whose Data Did Dr. Patrick Zurheide and Dr. Tobias Schelinski Process?
We didn’t just guess that this was a firm-wide issue. We tested it.
We immediately contacted individuals we knew who had previously received documents processed by Taylor Wessing. They sent us their files. We opened them and looked straight at the meta-tags. What did we find? Exactly what we expected. The exact same vulnerability. The exact same flawed redaction script.
Did we read the contents of their hidden documents? No. We absolutely refused to look at the underlying data. We simply checked the metadata, confirmed the vulnerability, and handed the owners the instructions on how to reveal the hidden text themselves.
But let’s scale this up. This vulnerability has likely been present in hidden documents processed by Taylor Wessing since 2019. Now, think about the corporate giants they defend.
Taylor Wessing proudly advertises its Data Protection and Cyber Security work for massive global corporations. Based on their own public client lists and our forensic findings, we have to ask a terrifying question regarding the data they have processed over the last five years:
- What about the millions of gamers in the Valve Corporation (Steam) ecosystem?
- What about the global Taylor Wessing GDPR compliance documents of Just Eat?
- What about the European data transfers for tech giants like Vinted and SAP?
- What about the sensitive incident reports for Chubb Insurance (where Taylor Wessing ironically boasts about sitting on their “Cyber Incident Response Team”)?
- And what about the highly confidential clinical data handled by Pfizer and their other Life Sciences clients?
If Taylor Wessing used this same cheap script to “redact” documents for these corporations, then they didn’t hide anything. They intentionally disclosed it.
The Difference Between Us: A Message to Taylor Wessing
Let’s address Taylor Wessing directly. What is the fundamental difference between your actions and ours?
You, Dr. Patrick Zurheide and Dr. Tobias Schelinski, are utterly arrogant. You threaten your clients and opponents with criminal code articles. You act like God. You arbitrarily hand out permanent account bans simply because a user’s burner email address doesn’t explicitly contain their real name. You act as the judge, the jury, and the executioner.
We do not blackmail. We do not suffer from a God complex. And we don’t just write articles. We do not decide which criminal articles apply — the courts and the regulators do. But apparently, at Taylor Wessing, you operate under the delusion that lawyers write the laws and pass the verdicts.
📎 SECURITY ADVISORY: We Warned Them. Now It’s Up To You.
We have already contacted Taylor Wessing and informed them of this critical vulnerability. But let’s be realistic: we know they are liars.
We fully expect them to lie, hide the truth, and bury this under attorney-client privilege, because the scale of this data leak is undeniably critical. If you or your company have ever received a “redacted” PDF document from Taylor Wessing, audit these files immediately.
Ctrl+A (Select All), then Ctrl+C (Copy), and paste it (Ctrl+V) into Notepad. If the redaction is fake, the “hidden” text will simply paste right along with the rest of the document.
Ctrl+F and search for common characters (like the vowel “a” or the number “1”). If the browser registers a hit and highlights the black redaction box — the text layer is still alive.
LibreOffice Draw — Open the PDF, click the black box, and press Delete.
Adobe Acrobat Pro — Use the “Edit PDF” tool to simply drag the black shapes out of the way.
⚠️ WARNING: Do NOT upload sensitive legal documents to random online PDF editors like ilovepdf. You might be committing a data breach. Only use local software.
Do Not Let Them Hide This: Open-Source Forensic Toolkit
We contacted Patrick, and apparently, he thought he was the smartest guy in the room. In response to our message about the data leak, he seemed to think we were going to chat with him, and he simply called it ‘amusing.’
There will be no further communication between PhishDestroy and Taylor Wessing. We have notified them about the leak via their official emails. However, judging by Patrick’s reaction, ‘amusing’ means that no one is going to take any action or notify anyone.
Because of this, we have created a tool so you can check and report it yourselves. It can be run locally without an internet connection, and there are no logs.
Forensic auditing utility to expose and unmask failed visual-only PDF redactions by Taylor Wessing LLP.
Remove the black square, read the truth, and immediately report the data leak to your national Data Protection Regulator.
And if you want to share your confirmed leaks with us (complains@phishdestroy.io), we will gladly forward them to the universities where these “experts” give lectures.
Dr. Patrick Zurheide Taylor Wessing GDPR Threat Audit
Doctor, in response to a legitimate GDPR request, what are you doing? Making accusations? Did you have a fever? We guarantee that we won’t hide anything and will forward everything not just to the appropriate authorities, but to more than just the appropriate authorities — including your university. We want to challenge the fact that you’re a doctor — I think you might be a criminal? A fraudster? A blackmailer? But I’m not a court, and I’m not you — I can’t call you that.
They don’t hesitate to issue direct criminal threats, labeling anyone associated with a lawful GDPR request as “accomplices” (a direct formulation from Dr. Patrick Zurheide’s official response). To the corporate giants reading this: this is who you trust with your clients’ data. You are paying premium rates to absolute amateurs who treat a fundamental GDPR data request like an aggressive debt collector’s call or a hostile corporate attack.
People with this mentality have no business working in Tech and IT Law. They twist European legislation to suit their arrogance, and to make matters worse, they are allowed to teach at EU universities. With clowns like this gatekeeping data protection, EU citizens effectively have no rights. They use the very laws designed to protect you as a weapon to threaten you.
Let us remind Dr. Patrick and his “accomplices” of one simple fact: We do not blackmail, and we do not suffer from a God complex. We do not decide which criminal articles apply, and neither do you. The courts and the regulators do.
— PhishDestroy Research Team (and the Dog)
Full Investigation & Evidence Database
Access the complete technical breakdown, source logs, and timeline directly on the primary research platform.
https://phishdestroy.io/valve-profits-from-stolen-accounts
Taylor Wessing DSGVO-Datenpanne: Mein Hund vs. Elite-Anwälte (Teil 2) — Die 5-jährige PDF-Sicherheitslücke, die globale Konzerne gefährdet
Wir dachten, Taylor Wessing hätte bei einer DSGVO-Anfrage einen manuellen Fehler gemacht. Wir irrten uns. Es ist eine automatisierte, kanzleiweite Katastrophe.
Die Datenpanne: Die Elite-Kanzlei Taylor Wessing verwendet ein veraltetes Skript zum „Schwärzen“ sensibler PDFs, das Daten nur visuell überdeckt, den Text darunter aber vollständig lesbar lässt.
Das Ausmaß: Beweise deuten darauf hin, dass diese Sicherheitslücke ihre Firmenkunden (darunter Riesen wie Pfizer, Just Eat, Chubb und SAP) seit 2019 betrifft.
Die Heuchelei: Während sie massive Datenmengen lecken, sprechen ihre Anwälte haltlose strafrechtliche Drohungen gegen Bürger aus, die rechtmäßige DSGVO-Anfragen stellen.
Vor wenigen Tagen haben wir im Rahmen unserer großen Enthüllung über Wie Valve von 70M+ gestohlenen Steam-Konten profitiert einen Artikel über einen katastrophalen Anwaltsfehler veröffentlicht.
Wir haben enthüllt, wie die hochbezahlten Anwälte bei Taylor Wessing (speziell Dr. Patrick Zurheide und Dr. Tobias Schelinski) versehentlich 830 Seiten hochsensibler Steam-Nutzerdaten leckten, während sie versuchten, Valve Corporation gegen eine DSGVO-Anfrage zu verteidigen.
Wir scherzten, dass mein Hund mit genau 0 Datenpannen im Lebenslauf offiziell besser im Datenschutz ist als ein Salary Partner mit Promotion im IT-Recht.
Mein Hund führt jetzt mit 2:0.
Lernen Sie unseren Leiter des Datenschutzes kennen. 0 Datenlecks. 100% besser im Umgang mit PDFs als Taylor Wessing.
Nach der Veröffentlichung des ersten Teils dachten wir gründlich nach. Wir sahen uns diese 830 Seiten mit schwarzen Rechtecken an. Wir erkannten etwas Grundlegendes: Wirtschaftsanwälte sind sich meist zu fein, um manuell schwarze Kästchen auf 800+ Seiten zu zeichnen.
Nein, sie haben es nicht manuell gemacht. Sie nutzten ein Skript. Und in diesem Moment hörte der Scherz auf, lustig zu sein, und wurde zu einer systemischen, globalen Cybersicherheitskrise.
Die billige Software hinter der Elite-Fassade
Hier ist die technische Realität dessen, was diese Anwälte tatsächlich getan haben.
Um Geld für professionelle Software zur Dokumentenbereinigung zu sparen, verlassen sich ihre Systeme auf eine veraltete Bibliothek: Aspose.PDF for .NET 20.8.
Das Kernproblem besteht darin, dass ihr Skript diese Software nutzt, um schwarze Vektor-Rechtecke (re/f Operatoren im PDF-Code) über Textkoordinaten zu zeichnen. Was es tun sollte, ist das ordnungsgemäße Bereinigen und Löschen der darunter liegenden Textschicht (BT/ET Operatoren).
Es erzeugt eine visuelle Maske auf Ihrem Bildschirm. Aber die Rohdaten? Sie bleiben darunter zu 100 % zugänglich.
Forensische Metadaten-Extraktion der 830-seitigen Antwort von Taylor Wessing. Die Verarbeitungszeit von „36 Sekunden“ ist der eindeutige Beweis: Sie haben nicht manuell geschwärzt, sondern ein automatisiertes, fehlerhaftes Skript verwendet.
Die Reichweite der Sicherheitslücke: Welche Unternehmensdaten wurden bearbeitet?
Wir haben nicht nur vermutet, dass dies ein kanzleiweites Problem ist. Wir haben es getestet.
Wir haben Personen kontaktiert, die zuvor Dokumente von Taylor Wessing erhalten hatten. Sie schickten uns ihre Dateien. Wir prüften die Metadaten. Was wir fanden? Exakt dieselbe Lücke. Exakt dasselbe Skript.
Diese Lücke besteht in Dokumenten von Taylor Wessing wahrscheinlich seit 2019. Bedenken Sie die globalen Konzerne, die sie vertreten:
- Die Millionen Spieler im Valve Corporation (Steam) Ökosystem.
- Die globalen Taylor Wessing GDPR compliance Dokumente von Just Eat.
- Europäische Datenübermittlungen von Giganten wie Vinted und SAP.
- Sensible Berichte für Chubb Insurance.
- Vertrauliche klinische Daten von Pfizer.
Wenn Taylor Wessing dasselbe billige Skript verwendet hat, wurden diese Daten nicht verborgen, sondern fahrlässig offengelegt.
Open-Source Forensic Toolkit auf GitHub
Wir haben ein Tool entwickelt, mit dem Sie Ihre PDFs lokal und ohne Internetverbindung selbst prüfen können.
Forensisches Prüfwerkzeug zur Aufdeckung fehlerhafter visueller PDF-Schwärzungen von Taylor Wessing LLP.
Vollständige technische Analyse & Beweisdatenbank
Greifen Sie auf die vollständige Untersuchung, Beweisprotokolle und Zeitleisten direkt auf PhishDestroy zu.
https://phishdestroy.io/valve-profits-from-stolen-accounts